A lot of small Edmonton offices are already in the cloud. They just don't call it that yet.
It usually looks messy up close. Two people share a Dropbox login. The owner checks Microsoft 365 mail from a home laptop. QuickBooks lives in one place, scanned PDFs live somewhere else, and the old office server still hums under a desk through another Prairie winter because nobody wants to touch the thing while tax season, payroll, or quoting is underway.
That's where cloud service integration really starts. Not when a vendor demo ends. Not when someone buys a subscription. It starts the day a business admits the current setup works only because everyone remembers the workarounds.
Table of Contents
- Starting Point for a Cloud Integration Project
- Inventorying Applications, Data, and Residency Needs
- Choosing Cloud Providers and Integration Patterns
- Migrating Workloads Without Breaking the Business
- Hardening Network, Identity, and Access Controls
- Backup, Recovery, and Ongoing Support
- Keeping Your Cloud Environment Healthy Over Time
Starting Point for a Cloud Integration Project
A four-person accounting office in south Edmonton is a familiar example. One staff member saves client files to a local shared folder. Another uploads copies to Dropbox so they can work from home. The owner uses Office 365 on a laptop that also has a pile of files on the desktop. The internet goes down once, and suddenly nobody knows which copy is the one.
That isn't a product problem. It's an operating model problem.
Write down what hurts before you buy anything
The first useful step is plain and unglamorous. Take a sheet of paper or a spreadsheet and list what's hurting today.
- Shared passwords: Who's using one login for multiple people, and where?
- Duplicate files: Which folders exist in more than one place?
- Single points of failure: What breaks if the under-desk PC dies tomorrow?
- Owner dependency: Which systems only one person knows how to access?
- Six-month risk: If nothing changes for six months, what's most likely to fail first?
When I'm on site, this is the moment where the project shows up. The cloud piece is usually the easy part. The hard part is untangling ownership, access, and years of little exceptions.
Practical rule: If nobody can say who owns a system, that system is not ready to be integrated.
Use a dependency and residency lens from day one
Every later decision should pass through two filters.
First, dependency. What relies on this system? A mailbox may also handle invoicing alerts, scanner notifications, password resets, and calendar booking. A file share may feed a line-of-business app, not just store documents.
Second, data residency. Where can the data live, and where can connected tools process it? Canadian businesses often assume a Canadian tenant means every connected service stays in Canada. That assumption can fail fast once outside connectors, analytics tools, or third-party OAuth apps get involved.
For larger migrations, I like resources that focus on application relationships instead of just “move it all” thinking. This ERP cloud migration from Kagool is useful because it frames migration around business systems and sequencing, which is how these projects survive contact with real users.
For smaller firms, the first milestone is simpler. Get the current environment mapped well enough that every later choice has context. If you need hands-on planning around networks, cloud setup, and support for a small office, business IT solutions are one way to structure that work without pretending every company needs a full enterprise rollout.
Inventorying Applications, Data, and Residency Needs
Before touching a single cloud account, do a discovery pass on site. Open the server cabinet, check the workstations, inspect the router, review subscriptions, and ask where staff save files. Memory is unreliable. Screens and devices tell the truth.
A proper inventory should capture both what people use every day and the background services they forget exist until they fail.
What to inventory first
Start with these categories:
- Line-of-business applications: QuickBooks, practice management tools, POS systems, CRM platforms, scheduling software, and any app that stores customer or financial records.
- File locations: Local drives, shared folders, NAS units, Dropbox, OneDrive, Google Drive, USB drives, and scanned document folders.
- Identity systems: Microsoft 365 accounts, Google Workspace accounts, local Windows logins, Apple IDs used for business, and admin accounts that nobody has reviewed in years.
- Network dependencies: Firewall, Wi-Fi gear, VPN, DNS, printers, scanners, and any always-on workstation acting like a mini server.
- Backup and recovery tools: Local backup drives, platform recycle bins, sync clients, image backups, and cloud backup products.
- Residency-sensitive data: HR records, accounting files, health information, legal files, customer databases, and anything tied to contractual or regulatory handling requirements.
The most useful question beside every item is the same one. What depends on this, where can its data live, and what does downtime stop?
Shortcuts that cause trouble later
I see the same mistakes over and over.
One is trusting the office manager's recollection instead of validating accounts, licences, and devices directly. Another is skipping infrastructure because it feels “not cloud related.” Then cutover day arrives and the scanner can't send to email, the printer mappings break, or the firewall is still hanging onto old exceptions for software nobody should be using anymore.
Don't skip firmware review either. Cloud service integration often exposes old local problems that users had worked around.
The router, the copier, and the old backup drive are part of the cloud project whether anyone likes it or not.
Pre-Cloud Integration Inventory Worksheet
| Asset Category | Examples | Owner | Data Residency Requirement | Outage Cost (per hour) |
|---|---|---|---|---|
| Email and identity | Microsoft 365, Google Workspace, shared mailboxes | Office manager, owner, outsourced IT | Note whether messages, contacts, and authentication data have contractual or policy constraints | Low, medium, or high based on missed client work |
| File storage | Local server share, OneDrive, Dropbox Business, NAS | Assigned staff member or department | Record where documents may be stored and whether connected apps move them elsewhere | Estimate by lost staff time and delayed deliverables |
| Business apps | QuickBooks Online, ERP, scheduling app, CRM | Department lead | Mark customer, financial, or regulated data handling needs | Note if invoicing, payroll, or service delivery stops |
| Network services | Firewall, Wi-Fi, DNS, VPN, printer scan workflows | Technician, provider, or owner | Usually indirect, but can affect access to residency-controlled systems | Often high because everything behind it is affected |
| Backup and recovery | Cloud backup tool, local image backup, archive drive | Named admin or provider | Confirm backup storage location and retention expectations | High if recovery is unclear or untested |
By the time this sheet is complete, you've got more than an inventory. You've got the scope document for the whole project.
Choosing Cloud Providers and Integration Patterns
Provider choice gets overcomplicated fast. Most small businesses don't need a philosophy about cloud. They need a stack that matches how they already work, what data they handle, and who will support it after the dust settles.
The wrong pattern is easy to spot. A business buys three cloud platforms because each one looked good in a demo, then ends up with more passwords, more sync conflicts, and more places where permissions drift.
Compare the provider categories, not just brands
| Provider Category | Typical Use Case | Integration Pattern | Best Fit For | Watch-Out |
|---|---|---|---|---|
| Hyperscaler productivity suites | Email, calendaring, documents, identity | Native identity, device management, file sync, shared collaboration | Offices already centred on Microsoft 365 or Google Workspace | Can become bloated if every workload gets forced into one ecosystem |
| Specialist SaaS | Accounting, document signing, project tools, industry apps | API connector, SSO, export/import, vendor-native add-on | Firms with strong line-of-business software needs | Each extra SaaS tool adds another access and governance surface |
| Integration glue | Identity sync, workflow automation, managed connectors | SSO, app-to-app automation, central policy and logging | Businesses with multiple apps that need controlled data flow | Easy to create hidden dependencies nobody documents |
One useful benchmark in Canada is that hybrid and multicloud setups are common, but they often aren't well integrated. An IDC/CDW survey found 59% of organizations planned to use multiple public clouds over the next two years, while 34% reported little to no interoperability between those environments (IDC/CDW survey). That tracks with what technicians see on the ground. Two clouds can be fine. Two clouds with no shared identity, logging, or policy discipline become a support headache.
What a small office should actually use to decide
A non-technical owner can still make solid decisions by asking a short set of practical questions:
- Where is the business already anchored? If staff already live in Outlook, Teams, Word, and OneDrive, forcing a pivot to another suite may create more friction than value.
- What do current licences already include? Many firms pay for features they never turn on.
- Does a second cloud solve a real problem? Sometimes it adds capability. Sometimes it just adds another admin portal.
- Can local support staff verify and maintain it? A good design has to survive regular support, not just migration week.
For owners weighing Microsoft, Google, and the major infrastructure platforms by workload, this workload cloud selection advice is a reasonable outside read because it compares fit by use case instead of treating every provider as interchangeable. If your office leans toward Google for collaboration, a practical starting point is proper Google Workspace setup with identity, sharing, and device controls configured cleanly from the start.
Migrating Workloads Without Breaking the Business
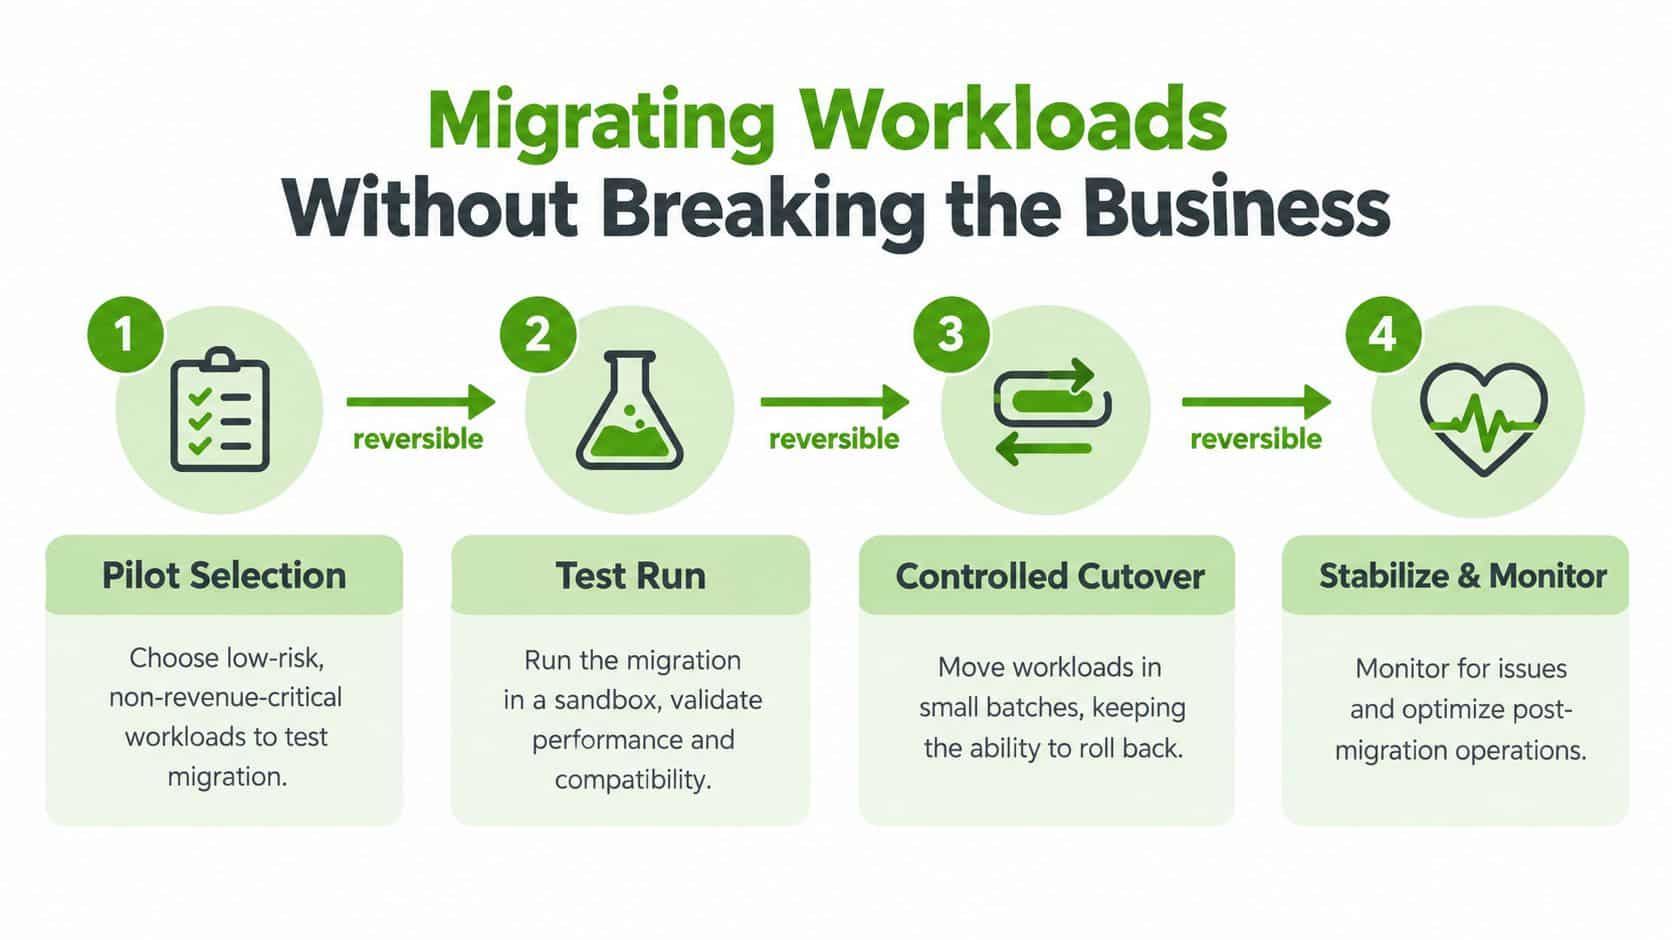
Migrations fail when people treat cutover like a switch flip. A safer model is staged, reversible, and documented well enough that a tired owner can still follow what happened after the fact.
Pick one workload that matters enough to reveal real problems, but not so critical that a rough edge stops the business cold. Shared calendars, user mailboxes, a working document set, or a small department file share usually make better pilots than payroll, the main accounting system, or the owner's only laptop.
Pick a pilot that teaches you something
A good pilot does four jobs at once. It tests sign-in, file access, permissions, and one real business workflow.
Choose something with these traits:
- Low revenue risk: If it misbehaves, staff can still work around it for a short window.
- Real integrations: It should touch printers, mobile devices, shared folders, or another SaaS platform.
- Representative users: Pick staff who use the system heavily, not the lightest user in the office.
- Contained rollback: You can put the old setup back into service without rebuilding from scratch.
A practical migration story that gets this sequencing right is this achieving cloud transformation case study. The value isn't the industry. It's the reminder that transformation works better when the move is staged around operations, not branding.
Use verification gates at each stage
Move in layers. Pilot user first. Then a department. Then the full tenant or broader workload group.
At each stage, verify a short checklist before moving on:
- Authentication works: Staff can sign in without odd prompts or account loops.
- Mail flow is normal: New messages arrive, send correctly, and shared mailbox access still works.
- Permissions survived: Team folders, calendar delegation, and department shares match what users had before.
- Printing and scan workflows still function: A lot of “successful” migrations fail.
- Third-party connectors still hold tokens: Billing apps, CRM connectors, scanners, and signature tools often need reauthentication.
- Time and locale settings match reality: A wrong time zone can break bookings, audit trails, and automated reminders.
Don't call a phase complete because the admin portal looks tidy. Call it complete when users can do their ordinary work without inventing new workarounds.
Define rollback before cutover starts
Rollback isn't pessimism. It's professionalism.
Keep the source environment readable for a defined window. Save last-known-good records and configuration notes. Document who holds admin credentials and where those credentials are stored. If files need to be repopulated locally, pre-stage the script or procedure before the move, not after the panic call.
A simple cutover-day runbook works well in this format:
- T-7: Confirm inventory, user list, admin access, test accounts, and communications.
- T-1: Freeze unnecessary changes, verify backups, export critical settings, notify staff.
- T-0: Execute cutover, validate login, mail flow, file access, and device sync.
- T+24: Review support issues, permissions, scanner flows, and mobile prompts.
- T+72: Finalize exceptions list, close rollback window where appropriate, record lessons learned.
That structure keeps cloud service integration auditable and reversible, which matters because something almost always behaves differently once real users touch it.
Hardening Network, Identity, and Access Controls
The first week after cutover is usually when the weak spots show up. Staff are signing in from home, phones start prompting for old credentials, and someone shares a folder a little too broadly because they need an answer fast. From a technician's side, this stage is less about admiring the new tenant and more about proving that the right people can work, the wrong people cannot, and every exception is intentional.
Provider defaults rarely match how a small Edmonton office operates. They are built to get users active quickly. Hardening is the work of turning a usable cloud setup into one you can hand back with clear rules, traceable access, and fewer easy mistakes.
Identity comes first
Identity is still the control that carries the most weight. If sign-ins are loose, everything behind them is loose too.
For a small office, that usually means setting a short list of rules and then checking them account by account:
- MFA for every user: Start with email, file storage, admin portals, payroll, and finance tools.
- Separate admin accounts: Tenant administration should sit on a different account than day-to-day email and Teams or Google Workspace use.
- Legacy authentication disabled: POP, IMAP, and older sign-in methods still cause trouble if they are left on for convenience.
- Conditional access based on reality: Limit admin access by country, require stronger checks for risky sign-ins, and decide whether unmanaged personal devices get full access, web-only access, or no access.
In practice, I verify this with test accounts, a non-admin user, and at least one mobile device on cellular. If a policy looks correct in the portal but fails in the field, it is not finished.
Network and sharing controls still matter
Cloud integration changes the attack surface. It does not remove it.
A lot of small offices still have leftovers from the old setup. Port forwards stay open after the server is gone. Guest Wi-Fi can still see business devices. A scanner, NAS, or line-of-business PC remains on the local network and now talks to cloud services with almost no segmentation. Those are the details worth checking on site because they do not show up neatly in a cloud dashboard.
Good cleanup usually includes retiring old remote access rules, separating guest and business traffic, documenting any device that still has to remain local, and putting remaining access behind managed VPN or application proxy controls. DNS filtering at the firewall is also worth the effort for many small sites. It blocks a fair amount of bad traffic before the user needs to make a decision.
For data handling, set the tenant to the restrictive side first. Then open only the exceptions the business needs. External sharing, forwarding, and anonymous links cause a lot of avoidable mess in small environments because nobody meant to create risk. They just needed to send a file quickly.
What a hardened setup looks like in practice
| Control Area | Provider Default | Hardened Setting |
|---|---|---|
| User sign-in | Password-only access may remain available in some workflows | MFA enforced for all users, with stronger requirements for admins |
| Admin access | One account may handle both admin and daily work | Separate admin identities with least privilege applied |
| Device access | Personal and unmanaged devices may connect broadly | Conditional access rules limit risky or unmanaged device access |
| External sharing | Broad link sharing or ad hoc invites may be allowed | Tenant-level restrictions with named exceptions and review |
| Audit visibility | Basic logs may exist but go unread | Sign-in, mailbox, and file activity logs enabled and reviewed |
| Edge exposure | Legacy remote access rules can linger after migration | Old exceptions removed, remaining access paths documented and tested |
Logging matters here, but only if somebody checks it. Enable sign-in logs, mailbox auditing, file activity logs, and alerting that matches the size of the business. A five-person office does not need the same tooling as a larger firm, but it does need enough visibility to answer basic questions after an incident or an access dispute.
A practical support option for local businesses is ongoing monitoring rather than a full MSP arrangement. Nerds 2 You doesn't provide full MSP services but does provide ongoing support and network monitoring for small and medium businesses. That often fits firms that want someone to review policy drift, patch obvious gaps, and confirm that the controls put in place after migration still match how the office works months later.
Backup, Recovery, and Ongoing Support
Monday morning in an Edmonton office, somebody opens Outlook and half the shared folders are gone. The files were syncing on every machine on Friday, so the first reaction is usually, "They must still be in the cloud." Sometimes they are. Sometimes a deletion, overwrite, or ransomware event has already synced everywhere, and now the job is recovery, not troubleshooting.
That is why backup and recovery need to be treated as part of the operating model, not as a box checked during migration. On site, I want to leave a customer with three things I can verify before I walk out. Backups are running to an independent destination. Someone knows what gets restored first. Someone will notice when a job fails.
Backup means independent retention
Sync is for access. Backup is for recovery.
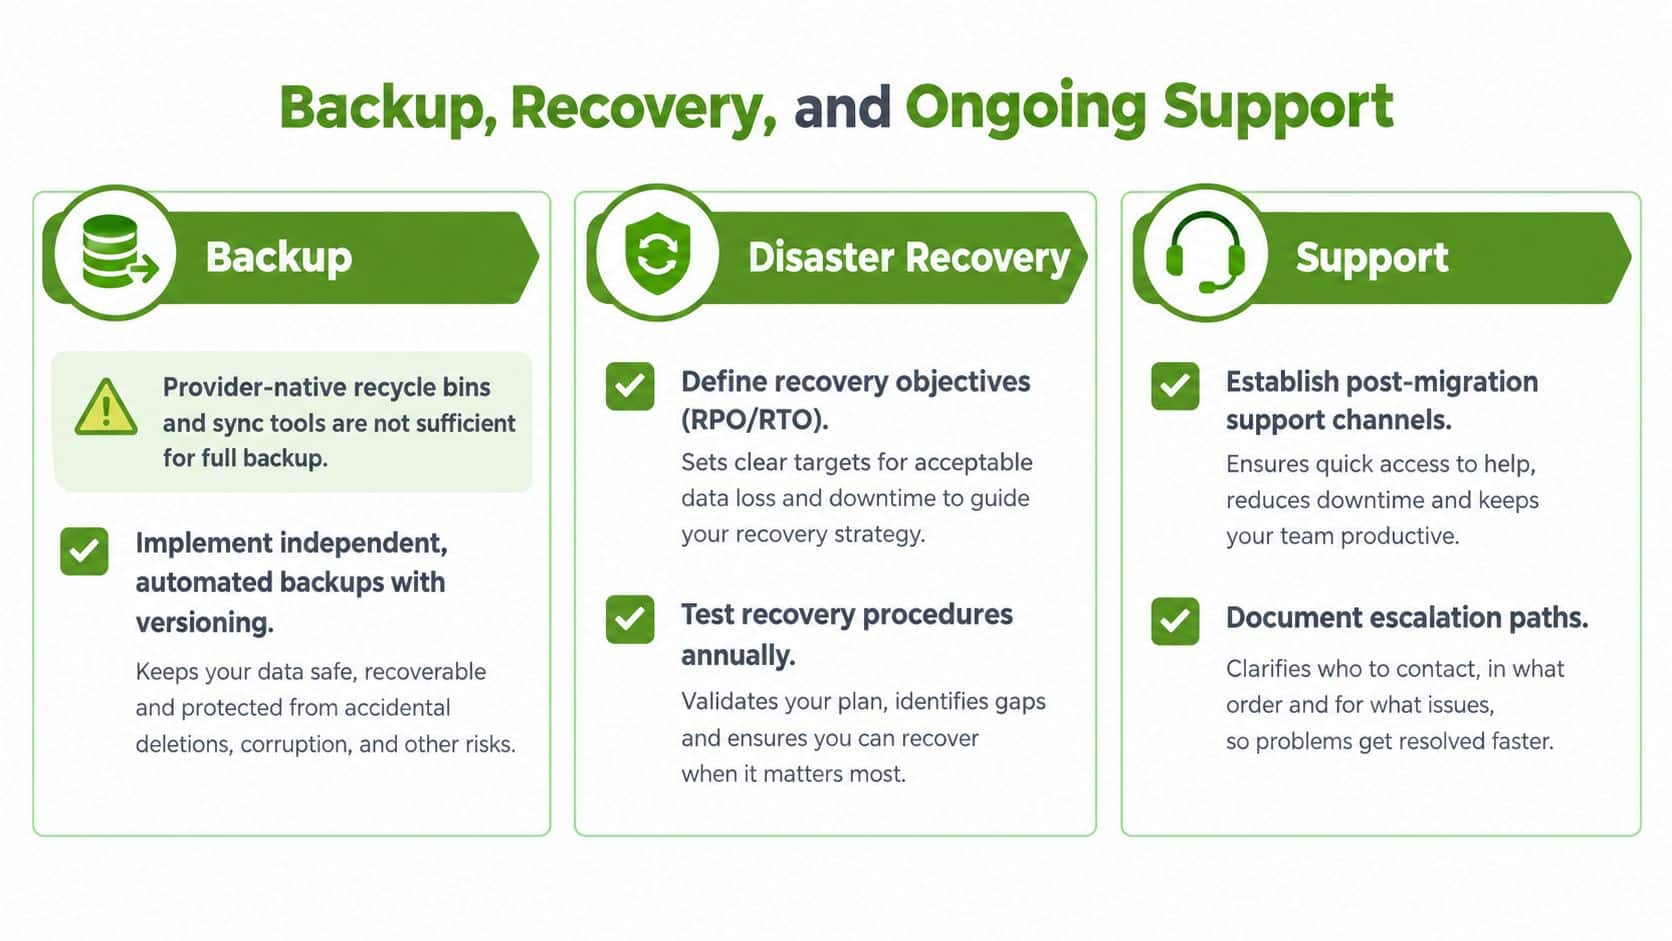
Provider recycle bins, file version history, and deleted-item retention all help, but they are still tied to the live service. If the wrong account wipes data, a bad rule purges mail, or encrypted files sync back into the tenant, those convenience features may not give the business enough room to recover cleanly.
A backup plan that works in the field usually includes:
- Independent copies: Stored outside the live sync path and separate from the primary tenant or device.
- Version retention: Enough history to recover from accidental overwrite, corruption, or delayed discovery.
- Immutable storage where it fits: Useful for ransomware exposure or high-value shared data.
- Job reporting somebody reads: Daily or scheduled checks for failures, skipped items, and storage warnings.
For small offices, hybrid setups are often the practical answer. Local recovery is faster for big file sets, and cloud retention helps if the office has a theft, fire, or hardware loss. If that is the direction, data backup solutions for local and cloud retention can be mapped to the workload instead of assuming the provider default is enough.
Recovery needs a tested runbook
Recovery targets have to be attached to real business tasks. A bookkeeper may need the accounting share back the same day. Archived marketing files can wait longer. Mail for the owner may be urgent. Old project folders may not be.
Write those priorities down by workload. Then attach a runbook that names the responsible person, where access credentials are stored, which systems come back first, and how staff confirm the restore is usable. I do not mean "the backup vendor says the job passed." I mean opening the restored mailbox, checking permissions on the shared folder, and confirming the line-of-business file launches.
A backup that has never been restored is still an assumption.
Ongoing support keeps recovery realistic
Support after migration is the part many small businesses underestimate. Cloud service integration keeps depending on local devices, office internet, DNS, endpoint health, and the staff changes that happen long after the move. Recovery plans drift when nobody updates them after a laptop replacement, a licence change, or a new shared mailbox.
The support work is fairly plain, but it matters. Confirm backup jobs still include new users and new folders. Check that retired devices are gone from backup scopes and management portals. Review storage growth before retention jobs start failing. Make sure the person expected to do the restore still has the right access and knows where the runbook lives.
Some firms want that wrapped into a larger provider relationship. Others just need periodic monitoring and cleanup tied to how the office runs. Canadian providers such as MSP Corp's managed network services frame that work around monitoring, issue response, provisioning, and firewall or VPN support. For a small office, the main question is simpler. Who is checking that the cloud side and the local side still match, and who gets the call when they do not?
Hardware failures still complicate cloud support. A dead SSD, a failing motherboard, or intermittent power issue can look like a sync problem until someone tests the machine properly. General field support can handle many on-site repairs, but component-level board work is a separate specialty, as outlined by Electronics Doctor's board-level repair services. That distinction matters because customers often report one problem, while the fix spans backup validation, endpoint repair, and user recovery steps across both the cloud tenant and the physical office.
Keeping Your Cloud Environment Healthy Over Time
Cloud service integration is maintenance work dressed up as strategy. The migration finishes. The operating rhythm doesn't.
A healthy environment usually follows a simple review cadence:
- Monthly access audit: Remove unused accounts, check admin roles, confirm offboarding cut access.
- Quarterly licence and cost review: Look for paid accounts nobody uses, duplicate storage, and idle services still billing.
- Semi-annual recovery drill: Restore something real and document the result.
- Annual architecture review: Re-check the design whenever a new vendor, branch, compliance need, or major app enters the picture.
Watch for drift, not just failures
Drift is what undoes a good deployment.
Look for unused admin accounts, public sharing that got enabled “temporarily,” unassigned licences still hanging around, and old devices that still authenticate even though they should be retired. Review sign-in logs, confirm backup completion reports arrived, and make sure former staff don't still have access through a forgotten SaaS account.
In Canada, public-sector cloud adoption shows why this ongoing model matters. Shared Services Canada's cloud services began with a Cloud Brokering Service in 2017 and a Cloud Advisory Service in 2022, and by fiscal year 2022-23 those services had been used by 91 organizations, including 43 federal partners, 40 mandatory and optional clients, and 8 organizations from other levels of government. Over the same period, expenditures rose from C$8.379 million in 2018-19 to C$28.607 million in 2022-23 (Shared Services Canada evaluation). The useful lesson for a small business is simple. Even large organizations treat cloud integration as an ongoing governed service, not a one-time move.
Call an on-site technician when the review cadence slips, when an audit turns up access or network issues you can't safely verify yourself, or when a new office, new app, or new compliance requirement forces a redesign. Remote-only administration can handle a lot. It can't replace physically checking what's plugged in, who's using it, and what changed in the office without documentation.
If your office is juggling Microsoft 365, Google Workspace, shared files, backups, and local network gear, Nerds 2 You Edmonton can help with on-site setup, troubleshooting, ongoing support, and network monitoring for small and medium businesses. They handle most major hardware repairs on site, don't provide remote services, and can help you turn a fragile cloud setup into something documented and supportable. Visit Nerds 2 You Edmonton to see what local on-site help looks like.
Contact Nerds 2 You for quality professional service
Experience the difference with our dedicated team of experts ready to assist you. Whether you need immediate support or have questions about our services, we are here to help. Reach out today and let us provide you with the reliable service you deserve. Your satisfaction is our priority and we guarantee a prompt response to all inquiries.
Discover more from Nerds 2 You
Subscribe to get the latest posts sent to your email.