A message lands on your phone while you're in line for coffee. Another hits the office PC five minutes later. Both look normal. One asks you to re-enter your password. The other says a file share has been updated. One click can hand over an email account, install malware on a laptop, or give an attacker a foothold inside a business mailbox.
That's why email security best practices work best as layers, not as one setting or one app. Good habits matter. Account protection matters. Device patching matters. So do spam filtering, domain authentication, access rules, backups, and recovery steps when something still gets through.
For Edmonton homes and small businesses, the practical order matters too. Start with the choices users make every day and the controls around the account itself. Then tighten the devices and email apps people use, add domain-level protection if you run a business domain, and make sure you can recover when a mailbox or machine goes sideways.
This guide covers PCs, Macs, iPhones, Android phones, personal email accounts, Microsoft 365 tenants, Google Workspace accounts, and small office setups. It also reflects the kind of help that makes sense locally. Nerds 2 You provides on-site help rather than remote services, and it doesn't provide full MSP services. For small and medium businesses, it does provide ongoing support and network monitoring. It also handles most major hardware repairs on site, but not board-level repairs.
Table of Contents
- 1. Enable Multi-Factor Authentication on Email Accounts
- 2. Implement Strong Password Policies and Management
- 3. Educate Users on Phishing Recognition and Email Security Awareness
- 4. Secure Email Clients and Keep Devices Patched
- 5. Use Email Filtering and Anti-Spam Solutions
- 6. Implement DMARC, SPF, and DKIM Authentication Protocols
- 7. Configure Email Access Controls and Enforce Usage Policies
- 8. Deploy Email Encryption for Sensitive Communications
- 9. Secure Email Backups and Data Recovery Procedures
- 10. Monitor Email Activity and Implement Logging for Audit Trails
- Top 10 Email Security Best Practices Comparison
- Turn the Checklist Into a Safer Email Routine
1. Enable Multi-Factor Authentication on Email Accounts
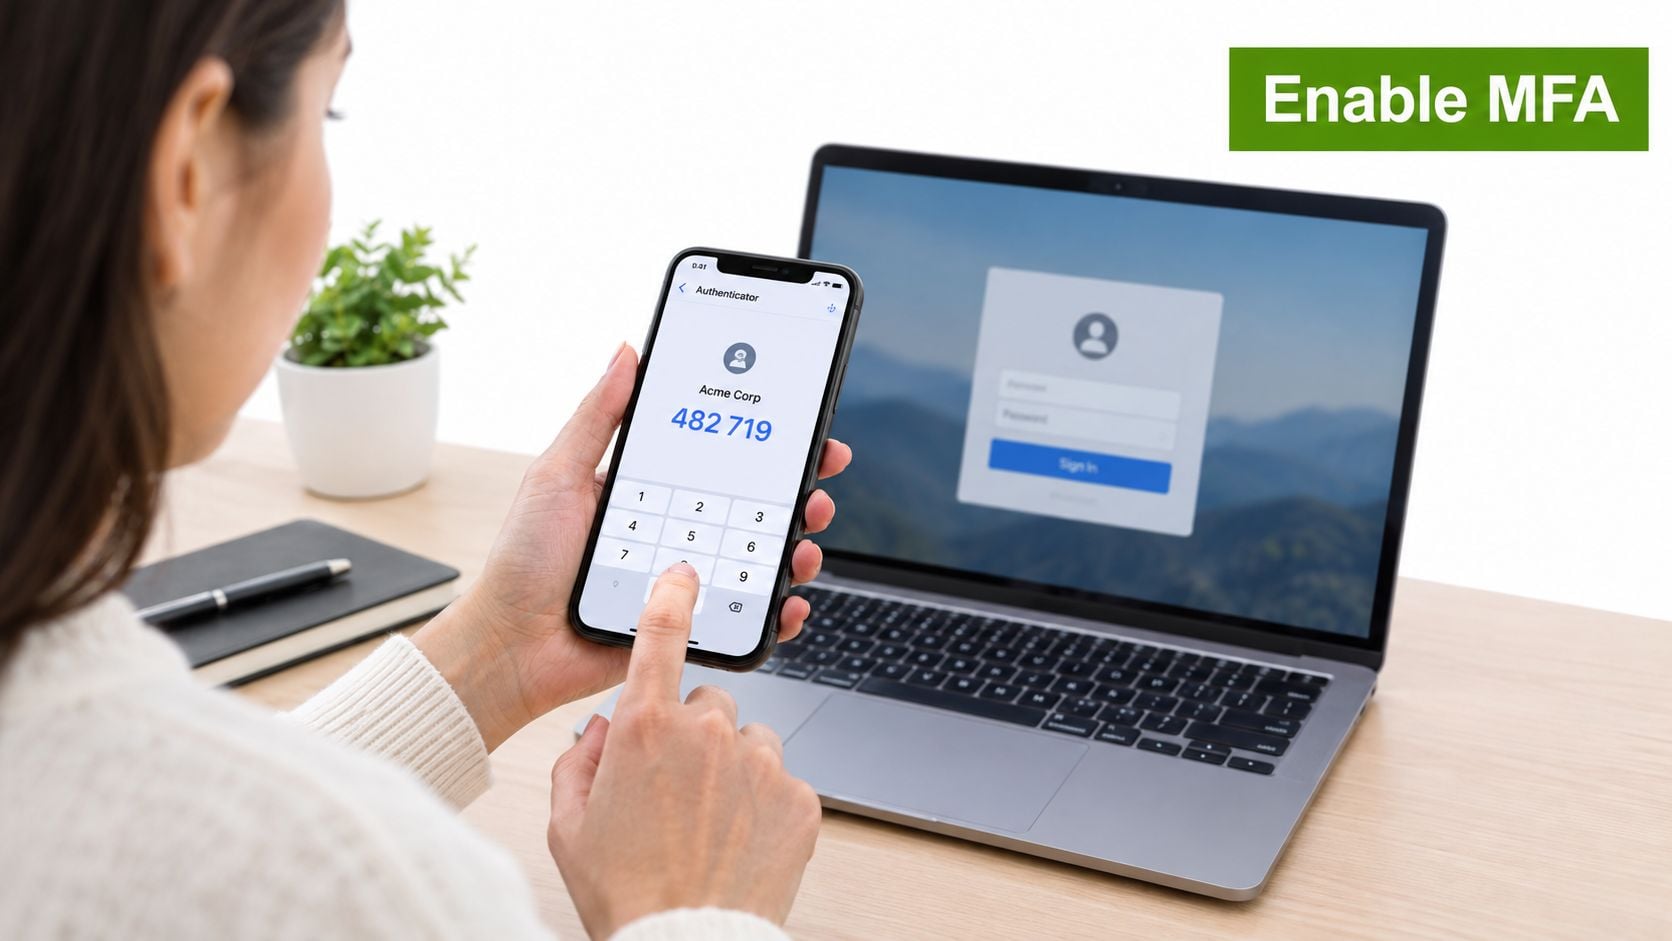
A strong password helps. MFA stops a lot more account takeovers because a stolen password alone isn't enough. For home users, that can protect a Gmail or Outlook account tied to banking, shopping, and password resets. For businesses, it can stop one compromised mailbox from becoming a company-wide problem.
Canadian federal guidance says to use MFA whenever possible for email, and its adversary-in-the-middle guidance says organizations should apply phishing-resistant MFA to all administrator accounts without exception in its email security best practices guidance. That matters because attackers don't just steal passwords anymore. They also try to intercept weaker sign-in flows.
What to turn on first
Start with the accounts that can do the most damage. Admin mailboxes, owner accounts, finance users, and anyone with password reset authority come first. On a home setup, secure the main email account you use to reset other services before anything else.
Practical rule: Use an authenticator app or a hardware-backed method before SMS when the platform allows it.
A few steps make MFA rollout less painful:
- Protect the recovery path: Save backup codes somewhere secure and offline enough that a mailbox compromise won't expose them.
- Test every device: Check sign-in on your Windows PC, MacBook, iPhone, Android phone, and tablet before you force everyone onto the new method.
- Remove shared logins: Shared accounts weaken MFA because nobody clearly owns the second factor.
- Get setup help if needed: If you want local hands-on assistance with account hardening, MFA setup support from Nerds 2 You fits that first-stage rollout.
MFA isn't the finish line. It's the first gate.
2. Implement Strong Password Policies and Management
A leaked shopping-site password can become an email breach in minutes if the same login was reused. For Edmonton households, that often means one personal mailbox exposes banking alerts, school accounts, and password resets for everything else. For a small business, one reused staff password can give an attacker access to invoices, vendor threads, and internal approvals.
Password policy works best as a priority list, not a lecture. Start with the mailbox that resets other accounts, then owner and finance accounts, then everyone else. The goal is simple. Every email login gets a unique password that nobody tries to memorize.
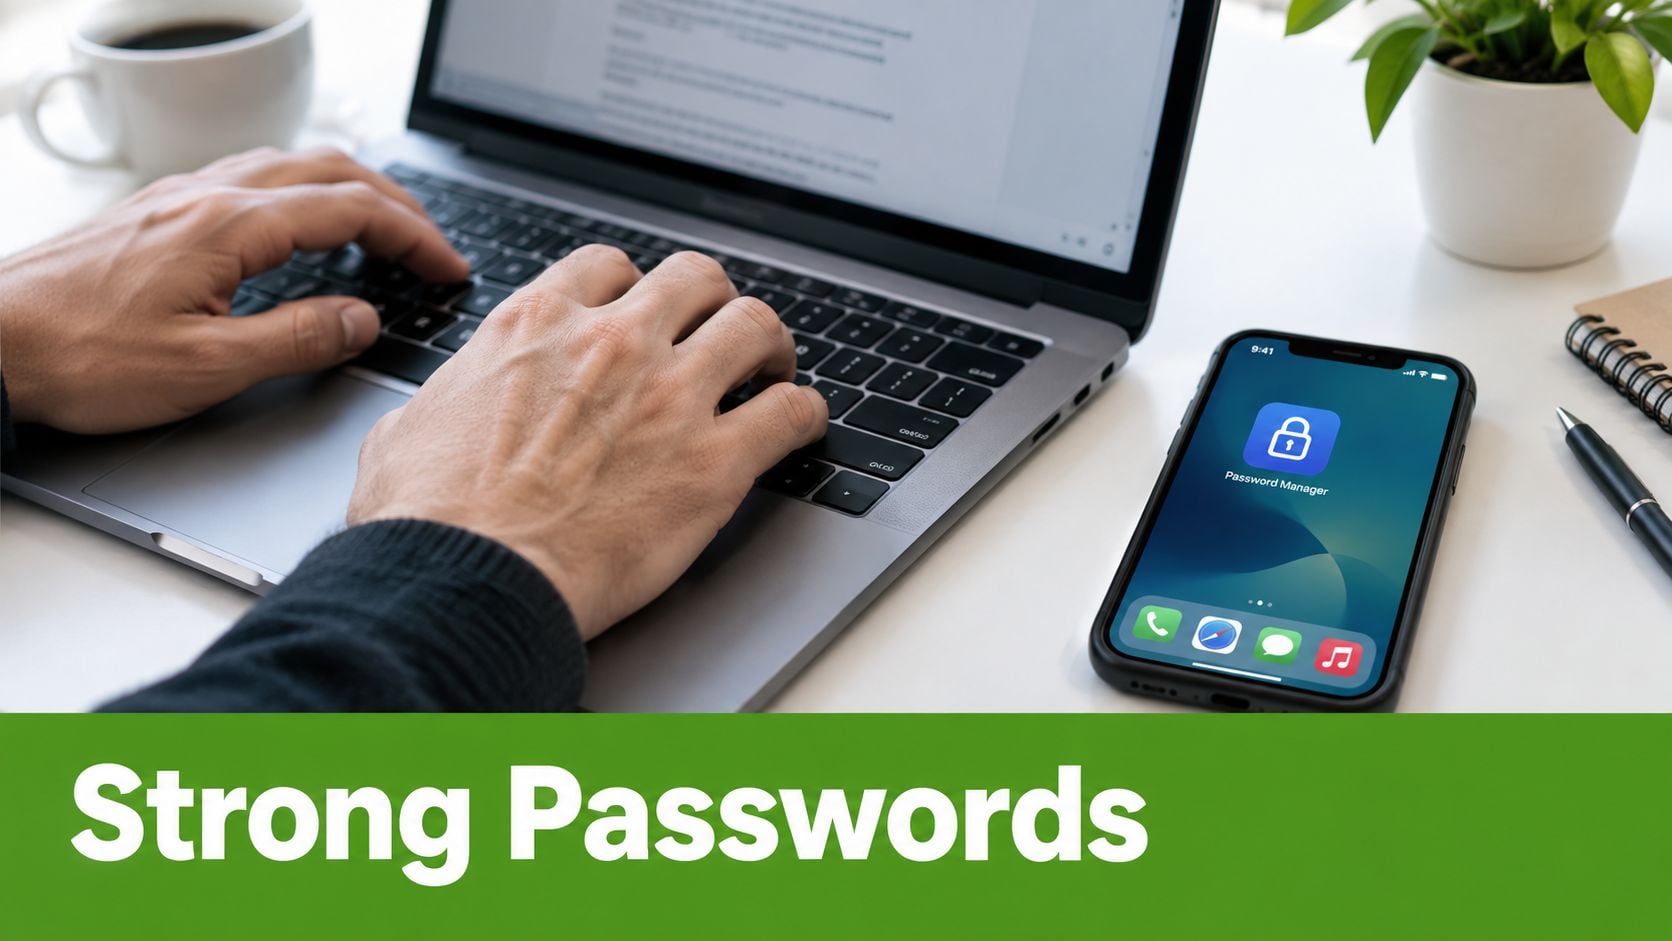
Long passphrases beat short, clever passwords. Unique beats memorable if you use a password manager. If you want a quick reference for current patterns, these strong password examples for 2026 are useful.
Here is the practical standard I recommend for home users and SMBs:
- Give each email account its own password. No reuse from streaming services, old forums, vendor portals, or another employee's shared login.
- Store credentials in a password manager, not in a notes app, spreadsheet, or shared browser profile.
- Turn off browser autofill on shared family computers and front-desk PCs where another person can open the session.
- Use secure vault sharing if two people must access the same service. Better yet, switch that service to a shared mailbox or named user accounts.
- Change passwords after a known compromise, staff departure, or suspicious login. Routine forced resets without a reason usually push people toward weaker choices.
There is a trade-off. Password managers add setup time and one more master credential to protect. In return, they cut down on reset requests, reused passwords, and the habit of writing logins on paper or saving them in the wrong place.
Device choice matters here. A personal iPhone with Face ID and a private laptop is a reasonable place to use built-in password tools. A shared Windows PC at reception is not. If staff sign in from multiple devices and nobody is sure where passwords are saved, that is usually the point where local on-site IT help makes sense. An on-site tech can check browsers, mail apps, saved credentials, and account ownership in one pass instead of guessing remotely.
3. Educate Users on Phishing Recognition and Email Security Awareness
A common Edmonton failure point is simple. Someone reads email on a phone in line for coffee, sees a Microsoft 365 alert or courier notice, taps fast, and hands over a password before the filter or IT person ever has a chance to help.
Phishing is still a user decision problem before it becomes a technical one. Good filtering catches a lot, but it will not catch every fake invoice, shared document notice, payroll request, or gift card scam. The goal is to give people a short checklist they can use on any device, especially phones where sender details and URLs are harder to inspect.
The Canadian Radio-television and Telecommunications Commission described the volume and variety of these reports in its Spam Reporting Centre publication, including private company impersonation, government impersonation, extortion scams, business email compromise, gift card scams, and advance fee fraud. Those are the same patterns homes and small businesses deal with every week.
A useful rule is this: slow down when the message tries to speed you up.
When I train staff or home users, I focus on five checks instead of a long policy:
- Check the request: Password reset, wire change, gift card purchase, invoice approval, and file share access all deserve a second look.
- Check the sender details: Display names are easy to fake. Open the full address and look for misspellings or odd domains.
- Check the path: Hover over links on a computer. On phones and tablets, press and hold if the mail app allows it, or open the site manually in a browser instead of tapping.
- Check the tone: Urgency, secrecy, and pressure are common because they push people past normal verification.
- Check outside email: If money, credentials, or sensitive files are involved, confirm by phone call, text, or your known company contact list.
That approach works better than annual awareness slides because it matches what people face in real inboxes. It also fits the article's order of operations. User judgment comes first, before client hardening, mail filtering, and domain authentication can do their part.
For homes, keep the routine simple. Decide who the cautious person is in the household, and make it normal to ask before opening attachments, approving sign-in prompts, or responding to billing notices. For a small business, pick one reporting path and repeat it often. Forward suspicious email to one mailbox, or tell staff exactly which person to contact before they act.
For practical examples that match common scam patterns, see this guide to phishing attack prevention for Edmonton homes and small businesses.
There is a trade-off here. More caution slows down approvals and invoice handling a bit. That is usually far cheaper than recovering a mailbox, reversing fraudulent payments, or explaining to customers why a compromised account sent fake messages under your name.
Local help makes sense once the confusion is consistent across devices or staff roles. If people cannot tell whether warnings are coming from Outlook, Apple Mail, Gmail, a browser pop-up, or a fake login page, an on-site technician can walk through real examples on the actual PCs and phones people use every day. That kind of hands-on review is often faster than remote advice, especially on shared office computers and mixed-device setups.
4. Secure Email Clients and Keep Devices Patched
A common failure point is the device itself. An Edmonton business can lock down the mailbox, train staff, and still get compromised because an old laptop opens a booby-trapped attachment in an outdated mail app. At home, the pattern is similar. A parent upgrades the password, but a retired phone still has the account signed in and never gets security updates.
Email security at this stage becomes device-aware. The question is not only "Is the account protected?" It is also "Which app opens the mail, on which device, and is that device still supported?"
For households, keep the target small. List every phone, tablet, and computer that can open the mailbox. Remove access from devices nobody uses anymore. If a device no longer receives Windows, macOS, iPhone, iPad, or Android security updates, stop using it for email that carries banking, school, or tax information.
For a small business, the practical risk is shared and forgotten hardware. Front-desk PCs, old MacBooks kept as backups, personal phones with work mail, and test accounts in Outlook often stay connected longer than anyone realizes. That creates extra entry points and makes incident cleanup slower.
A good check here is simple:
- Confirm the device is still supported: Unsupported systems should not connect to business email.
- Update the mail app and the operating system: Outlook, Apple Mail, Gmail, and the browser used for webmail all need current security patches.
- Turn on automatic updates where stability allows: Home users should usually leave them on. Small businesses may schedule updates after hours to avoid interrupting reception desks or accounting work.
- Review saved accounts and profiles: Remove old employee mailboxes, stale IMAP or POP setups, and demo profiles left behind during troubleshooting.
- Back up local files before major upgrades: This matters most on older Windows PCs and Macs that may store local archives or downloaded attachments.
The trade-off is straightforward. Automatic patching reduces exposure, but updates can break an older printer, a plug-in, or a line-of-business app. For a home user, that usually means a short interruption. For a small office, it can affect a full workday if nobody checked compatibility first. That is why I usually recommend a basic update schedule for businesses: patch routinely, but test any older software or shared workstation that people depend on.
Local, on-site help is sensible once the problem is tied to the physical device rather than the mailbox settings. Examples include a laptop that cannot finish updates, a MacBook with too little storage to patch properly, an Android phone that still holds a former employee's mail, or a PC that became unstable after malware cleanup. Nerds 2 You can handle most major hardware repairs on site, but not board-level repairs.
5. Use Email Filtering and Anti-Spam Solutions
A common failure point looks ordinary. A bookkeeper in Edmonton opens a supplier invoice, the sender name looks familiar, and the attachment gets through because the mailbox accepts almost any file type. Good filtering reduces how often a user has to make that call in the first place.
Canadian complaint trends show why this matters. Canadians submitted 414,630 complaints to the Spam Reporting Centre in 2024 to 2025, including government impersonation, extortion, private company impersonation, employment scams, and bank impersonation, according to the CRTC annual report and related summary. Filtering helps by screening sender reputation, attachment types, message patterns, and known phishing indicators before the message reaches the inbox.
The priority here is simple. Stop the low-quality mail first, quarantine the doubtful mail second, and leave users with fewer decisions to make.
For home users, the practical baseline is short:
- Use the spam and junk protection already included with Gmail, Outlook.com, iCloud Mail, or your ISP email.
- Leave attachment scanning on.
- Check the junk folder occasionally for banking, medical, school, or travel messages that were held by mistake.
- Mark phishing as phishing, not just delete, so the service learns from it.
Small businesses need a tighter setup because one bad message can affect payroll, vendor payments, or customer replies. Start with attachment rules. If the office never needs .exe, .js, .scr, or password-protected archive files by email, block them. Then assign someone to review quarantine daily on business days. Reception, admin, or office management can usually handle this if the process is documented and takes five minutes.
Filtering strength always has a trade-off. Aggressive settings catch more junk, but they also hold legitimate invoices, e-transfers, and portal invitations. That is usually an acceptable trade because a delayed message is easier to fix than a compromised mailbox, a fraudulent payment, or a PC infected through an attachment.
Device mix matters too. A household using phones and tablets may rely mostly on the mail provider's built-in junk controls. A small office with Outlook on Windows PCs, Apple Mail on MacBooks, and a shared front-desk mailbox often needs policy set at the mail service level so every device sees the same result.
On-site help makes sense once filtering rules are colliding with how the office works. Examples include a copier that scans to email and gets blocked, a legacy accounting workflow that depends on emailed attachments, or a front-desk team that cannot tell whether quarantine failures come from mailbox rules, the mail service, or the local device.
6. Implement DMARC, SPF, and DKIM Authentication Protocols
A spoofed message from your own domain creates a different kind of problem than ordinary spam. Customers trust it. Staff may trust it too. If your business uses a custom domain, these records belong on the shortlist because they help receiving mail systems verify whether a message that says it came from you did.
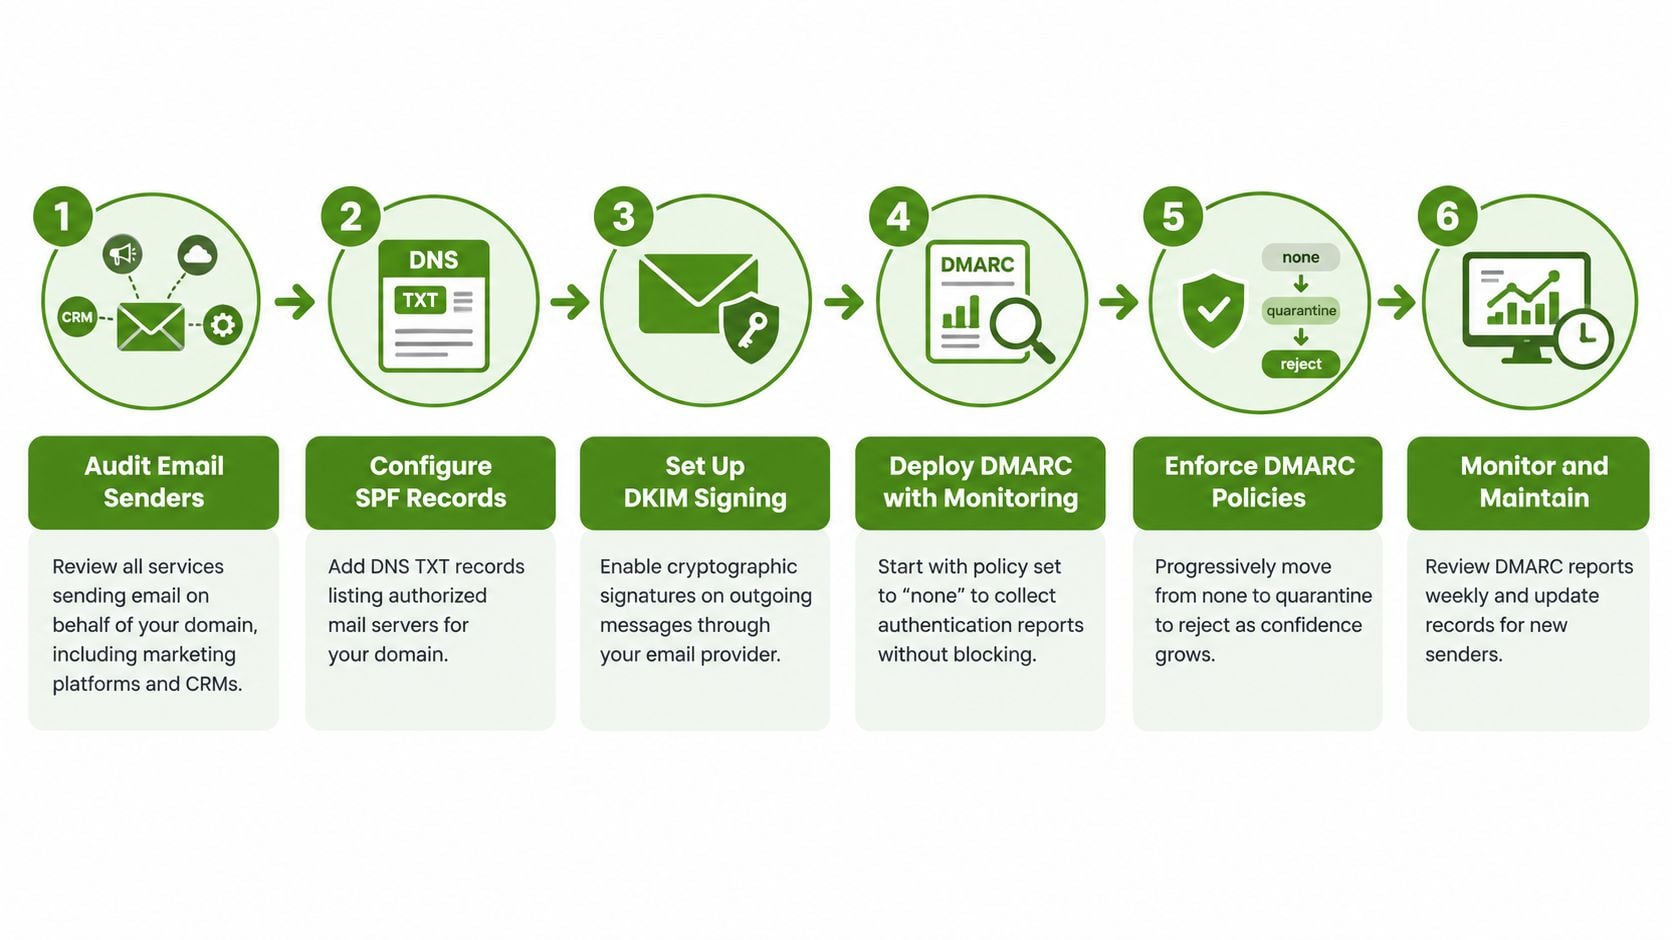
SPF lists which servers are allowed to send mail for your domain. DKIM adds a signature that shows the message was authorized and was not altered in transit. DMARC ties those checks to the visible From address and tells other mail systems whether to monitor, quarantine, or reject mail that fails. If you want a plain-language walkthrough of how the three fit together, this guide explains how to prevent spoofing with authentication.
The practical challenge is not publishing the records. It is finding every service that sends mail on your behalf before you tighten policy. Microsoft 365 or Google Workspace are obvious. Website contact forms, accounting platforms, booking tools, copiers, CRM systems, and newsletter services are where small Edmonton businesses usually get caught.
The Canadian Centre for Cyber Security quick guide to email configuration recommends setting up SPF, DKIM, and DMARC together, because DMARC evaluates the SPF and DKIM results. Its email domain protection guidance also explains that DMARC only passes when SPF or DKIM passes and aligns with the domain shown in the From field.
A sensible rollout looks like this:
- List every sender first: Include your main mail platform, website plugins, printers that scan to email, invoicing tools, and any third-party service that sends receipts, reminders, or campaigns.
- Publish SPF carefully: Keep it accurate and avoid piling in outdated services that no longer send mail for you.
- Enable DKIM on each active platform: This usually happens inside Microsoft 365, Google Workspace, or the vendor portal, not only in DNS.
- Start DMARC at p=none: Use reports to spot missing senders and alignment problems before enforcement.
- Move to quarantine or reject after testing: Tightening too early can block real customer replies, form notifications, or billing messages.
- Use local help if DNS changes are unclear: On-site support is sensible once multiple vendors, registrar access, and shared admin accounts are involved.
Home users on Gmail, Outlook.com, or another hosted address usually do not set these records themselves because the provider controls the sending domain. The check for a household is simpler. If email comes from a personal domain, ask the registrar or hosting company whether SPF, DKIM, and DMARC are already in place and who will maintain them after changes.
For a small business, this is one of the clearest examples of a trade-off between security and continuity. A strict DMARC policy cuts spoofing risk, but only after the sending inventory is complete. Take the time to map devices and services first. That step prevents avoidable outages and gives you a cleaner path to enforcement.
7. Configure Email Access Controls and Enforce Usage Policies
An Edmonton office manager approves invoices from a phone in the parking lot, a bookkeeper checks billing from a desktop at the shop, and a departing contractor still has mailbox access nobody removed. That mix is common. It also creates the kind of gap attackers use after they get into one account.
Access control decides who can read mail, send as another address, manage shared inboxes, approve changes, and create forwarding rules. Good settings reduce the damage from a stolen password or a mistaken click. Bad settings turn one compromised login into a company-wide problem.
Start with a simple rule. Give people the least access that still lets them do the job.
That sounds obvious, but small businesses drift away from it fast. Owners keep admin rights inside the same account they use all day. Staff share one mailbox password because it feels faster. Former employees stay on delegate lists because nobody wants to risk breaking workflow. Those choices save time for a week and create cleanup work for months.
A better approach is to separate access into a few decisions you can review without guesswork:
- Mailbox access: Decide who can open a mailbox and whether they need full access, send-as, or send-on-behalf permissions.
- Admin access: Keep tenant or domain administration on a separate account from daily email use.
- Shared inbox handling: Use managed shared mailboxes for addresses like info@ or support@ instead of passing credentials around.
- Forwarding and auto-rules: Limit who can create external forwards or inbox rules that move or hide messages.
- Approval steps: Require a second check for payment changes, banking updates, gift card requests, and sensitive document sends.
If you want a straightforward non-vendor overview, this article on practical RBAC implementation is a helpful starting point.
Policies should match the devices people use. If staff read email on personal phones, decide whether that is allowed, whether a screen lock is required, and what happens if the device is lost. If a front desk PC is shared across shifts, make sure each person signs in with their own account rather than using one mailbox profile all day. On paper, shared access can look harmless. On a real device, it often means no accountability and no clean audit trail.
For home users, the policy can stay short. Do not forward personal mail into multiple inboxes, avoid sharing a mailbox password with family members, and review account recovery options after life changes like a move, separation, or a child getting their own device.
For a small business, write down the rules in plain language and tie them to a real event. New hire. Role change. Departure. Lost phone. Vendor banking change. If nobody knows when access gets reviewed, it usually does not get reviewed.
Local support becomes sensible when the office has shared mailboxes, mixed Windows and Mac devices, staff using mobile email, and no clear owner for Microsoft 365 or Google Workspace administration. On-site help is also worth it if you suspect hidden forwarding rules, old delegate access, or former staff accounts that were never closed properly.
8. Deploy Email Encryption for Sensitive Communications
A payroll clerk sends T4 details to the right employee, but the address auto-completes to an older personal account. The message leaves in seconds. If that mailbox is no longer controlled by the intended recipient, the mistake is now a privacy problem, not just an email mistake.
Encryption reduces the fallout from that kind of error, but only if the method fits the people and devices involved. In practice, the order of decisions matters. Start by deciding which messages need protection, then choose the simplest option that works across the phones, laptops, and mail apps already in use.
A useful rule is to trigger encryption for content that would create real harm if sent to the wrong inbox. That usually includes HR files, financial records, contracts under review, ID documents, medical or benefits information, banking changes, and client records with personal details. Routine scheduling, general updates, and low-risk back-and-forth usually do not need the extra step.
For Edmonton home users, that often means using a provider's secure message option only for tax documents, legal paperwork, or scans of identification. For a small business, write the trigger into a short policy so staff do not have to guess. "Encrypt any message containing payroll, banking, government ID, or signed contract attachments" is clearer than telling people to encrypt sensitive email.
Tool choice matters less than consistency.
Built-in encrypted message features from Microsoft 365 or Google-based workflows are usually the easiest starting point because they work better across Windows, Mac, and mobile devices. S/MIME can be a good fit where both sides use compatible business mail systems and someone is prepared to manage certificates properly. Secure client portals are often better than email attachments when clients upload forms or download statements regularly.
Each option has a trade-off. Built-in provider encryption is easier for staff but may confuse recipients who are not used to secure message notifications. S/MIME offers tighter message-level control, but certificate setup, renewal, and recovery add admin work. Portals reduce attachment risk, but they add one more login and can slow down quick conversations.
Before rolling anything out, test a few real scenarios on the devices people use. Open an encrypted message in Outlook on Windows, Apple Mail on a Mac, an iPhone, and an Android phone. Confirm that attachments open, replies stay protected, and the recipient experience makes sense. If the process is clumsy on mobile, staff will work around it.
Two simple checklists help keep this practical.
For home users
- Use secure send options for tax forms, ID scans, legal documents, and financial records.
- Confirm the recipient address before sending attachments.
- Keep a readable copy of important records in a protected local or cloud location in case access to the encrypted message changes later.
For small businesses
- Define which message types require encryption.
- Standardize on one primary method unless a higher-risk case calls for something stricter.
- Test sending and receiving on every supported device.
- Assign one person to manage certificate renewal, secure message settings, and user support.
- Keep recovery access for keys, certificates, or protected files documented and limited.
Local on-site help becomes sensible when encrypted mail behaves differently across shared office PCs, personal phones, and mixed Microsoft 365 or Google Workspace setups, or when nobody is confident managing certificates and message rules. It is also worth getting hands-on support if staff have started bypassing the process by sending password-protected attachments over regular email, texting documents, or forwarding sensitive messages to personal accounts.
9. Secure Email Backups and Data Recovery Procedures
A mailbox can disappear in ordinary ways. Someone deletes the wrong folder. Outlook syncs badly after a device replacement. A Microsoft 365 or Google Workspace setting changes and old mail no longer shows up where expected. Recovery goes better when you decide in advance what needs to come back first, which device or service holds the clean copy, and who is allowed to restore it.
Cloud mail keeps data available, but availability is not the same as a backup plan. Retention rules, deleted items folders, and provider recovery options help with short-term mistakes. They do not always cover long retention needs, legal records, ransomware on synced devices, or a bad admin change that spreads across every mailbox.
Start with one practical question. If a key inbox vanished this afternoon, how would you restore the last 30 days, the last year, or only a few messages from a former employee or a family tax folder?
That answer should be different for different setups. A home user may only need provider retention plus a periodic export of important mail. A small business usually needs mailbox-level backups, clear restore permissions, and a written process for urgent recovery. If Outlook is part of daily work, this guide on how to back up Outlook emails gives a useful starting point.
A simple recovery plan usually covers four decisions:
- What gets backed up: entire mailboxes, shared mailboxes, contacts, calendars, and attachments
- Where the backup lives: provider tools, export files, third-party backup, or a mix
- Who can restore data: one owner is risky, too many admins is also risky
- How often recovery is tested: full mailbox restores and item-level restores are both worth checking
The trade-off is cost and complexity. More frequent backups, longer retention, and off-platform copies give better recovery options, but they also add admin work and another place to secure sensitive data. Backups need their own protection. Encrypt stored copies, limit restore rights, and keep the credentials for the backup system separate from the main email account where possible.
The Canadian Centre for Cyber Security makes a similar maintenance point in its ITSP.40.065 implementation document. Review the setup, correct errors, and keep it maintained over time. The same discipline applies here. A backup nobody has restored from is still an assumption.
For Edmonton homes and small offices, local on-site help starts to make sense during PC replacements, mailbox migrations, NAS setup, ransomware cleanup, and any recovery job involving multiple devices with different mail apps. Those are the moments where one wrong sync setting or export choice can overwrite good data. Hands-on support is also sensible if no one in the business can confidently answer a basic recovery question under pressure: what can we restore, from where, and how long will it take?
10. Monitor Email Activity and Implement Logging for Audit Trails
A common small-business breach starts with one bad click, then goes quiet. The attacker signs in, sets a forwarding rule to an outside address, and reads invoices, password resets, or client conversations in the background. No ransomware screen. No obvious outage. Monitoring is what turns that kind of quiet misuse into something you can catch.
For Edmonton households and SMBs, this part of the checklist sits late for a reason. Alerts do not replace good user decisions, MFA, patched devices, filtering, or access rules. They help confirm whether those controls are holding up, and they give you a record to review when something feels off.
Set your attention on a short list of events that usually matter:
- External forwarding or mailbox rule changes
- Sign-ins from a new device, city, or country
- Repeated failed sign-ins followed by a successful one
- Mailbox export activity or unusual bulk downloads
- Admin setting changes, especially on shared, finance, or owner accounts
Home users can often rely on built-in account activity pages and security alerts from Microsoft, Google, Apple, or their mail provider. Small businesses should go one step further and make sure logs are retained long enough to review an incident after the fact. If logs disappear after a short window, you may know an account was abused but have no clear timeline of what happened.
The trade-off is alert fatigue. Too many notifications train people to ignore the ones that matter. Start with high-risk events, test where the alerts go, and assign one person to review them on a schedule. For a five-person office, that may be a weekly check plus immediate review of forwarding-rule changes and suspicious sign-ins. For a home user, it may be as simple as keeping security alerts turned on and checking recent account activity after any phishing scare.
On-site help becomes sensible when the mail setup spans several devices, shared mailboxes, and more than one platform, or when nobody can tell which logs exist and who reviews them. In those cases, a local technician can verify that auditing is turned on, confirm where alerts are sent, and check that phones, PCs, and mail apps all line up with the same security expectations. That is less about buying a complex monitoring stack and more about making sure the evidence is there before you need it.
Top 10 Email Security Best Practices Comparison
| Item | 🔄 Implementation Complexity | ⚡ Resource Requirements | ⭐ Effectiveness | 📊 Expected Outcomes | 💡 Ideal Use Cases |
|---|---|---|---|---|---|
| Enable Multi-Factor Authentication (MFA) on Email Accounts | Medium, user enrollment + admin setup | Low–Medium, authenticator apps, optional hardware keys, support time | ⭐⭐⭐⭐⭐ | Dramatic reduction in account takeovers and phishing success | All users; prioritize admins, C‑suite, SMBs |
| Implement Strong Password Policies and Management | Medium, policy + roll‑out and training | Low, password manager subscriptions and admin time | ⭐⭐⭐⭐ | Fewer brute‑force and credential‑reuse incidents; stronger account hygiene | Individuals and SMBs with many accounts; enterprises |
| Educate Users on Phishing Recognition and Email Security Awareness | Low–Medium, ongoing training and simulations | Low, training platform or vendor, staff time | ⭐⭐⭐⭐ | Reduced successful phishing, stronger security culture | Remote teams, SMBs, regulated industries |
| Secure Email Clients and Keep Devices Patched | Low–Medium, enable + test updates across devices | Low, update mechanisms; higher for managed fleets | ⭐⭐⭐⭐ | Fewer exploitable vulnerabilities; improved stability | All endpoints; organizations with diverse OS environments |
| Use Email Filtering and Anti‑Spam Solutions | Medium, deploy and tune filtering rules | Medium, subscription costs, admin tuning | ⭐⭐⭐⭐⭐ | Blocks majority of spam/phishing; reduces malware delivery | High‑volume inboxes, customer‑facing businesses, SMBs |
| Implement DMARC, SPF, and DKIM Authentication Protocols | Medium–High, DNS configuration and testing | Low–Medium, DNS access, monitoring tools, expert time | ⭐⭐⭐⭐ | Prevents domain spoofing; improves deliverability and visibility | Organizations sending branded email, marketing, SMBs |
| Configure Email Access Controls and Enforce Usage Policies | High, RBAC design, policy drafting and enforcement | Medium–High, admin overhead, audits, IAM tools | ⭐⭐⭐⭐ | Limits unauthorized access; supports compliance and least privilege | Law firms, healthcare, finance, companies with sensitive data |
| Deploy Email Encryption for Sensitive Communications | High, key management and client integration | Medium–High, certificates/keys, training, support | ⭐⭐⭐⭐ | Ensures confidentiality and non‑repudiation; regulatory compliance | Legal, healthcare, finance, confidential client communications |
| Secure Email Backups and Data Recovery Procedures | Medium, backup configuration and testing | Medium, storage costs, backup solutions, testing time | ⭐⭐⭐⭐ | Rapid recovery from deletion/ransomware; retention for compliance | SMBs requiring retention, organizations prioritizing resilience |
| Monitor Email Activity and Implement Logging for Audit Trails | High, log aggregation, alerts, analysis | High, storage, SIEM/tools, trained analysts | ⭐⭐⭐⭐ | Faster detection of compromise; audit trails for investigations | Regulated organizations, larger SMBs, security‑minded enterprises |
Turn the Checklist Into a Safer Email Routine
The right way to use these email security best practices is to roll them out in the order that lowers risk fastest.
Start with account protection. Secure administrator accounts, owner accounts, finance users, and primary personal email addresses with MFA first. Then fix password reuse with a password manager and remove weak recovery paths. If a family member or employee can't explain how they'd recover their account after losing a phone, the setup isn't finished yet.
Next, improve user decisions and inbox hygiene. Train people to pause before acting on urgency, invoice changes, document shares, and password prompts. Tighten spam and attachment filtering so fewer risky messages ever reach the inbox. For many homes and SMBs, those first four actions reduce the most common problems without major disruption.
Then handle the systems side. Keep Outlook, Apple Mail, Windows, macOS, iOS, and Android devices patched. Review old accounts on retired phones and spare laptops. If you run a business domain, publish and tune SPF, DKIM, and DMARC properly. Shared mailboxes, access reviews, simple usage policies, and encryption for sensitive communications come after that.
Finally, protect recovery and visibility. Make sure mailbox backups are real, accessible, and tested. Turn on logging, review forwarding rules, and watch for suspicious sign-ins or mass exports. That's the layer that helps when prevention isn't enough.
If a suspicious message already got clicked, use a short incident routine:
- Stop interacting with the message: Don't reply, don't download more files, and don't keep testing the link.
- Change credentials from a trusted device: If possible, use a clean PC, Mac, or mobile device that wasn't part of the incident.
- Review active sessions and mailbox rules: Check sign-ins, forwarding rules, delegates, and recovery settings.
- Preserve the message: Keep the suspicious email for review instead of deleting all traces immediately.
- Notify affected people: If a compromised account may have sent messages to staff, clients, or family contacts, warn them quickly.
- Get help when the issue crosses devices or systems: Malware concerns, account takeover, and business domain problems often need hands-on support.
That's where local on-site service becomes sensible. If you're dealing with multi-device email setup, malware concerns after an attachment was opened, hardware trouble that affects a mailbox, backup recovery guidance, DNS authentication records, or small-business monitoring needs, Nerds 2 You Edmonton is one relevant local option. It provides on-site service, ongoing SMB support, and network monitoring. It doesn't provide remote services or full MSP services, and it handles most major hardware repairs on site but not board-level repairs.
A safer inbox usually comes from a handful of well-chosen controls, maintained consistently, on the actual devices people use every day.
Nerds 2 You Edmonton provides on-site help for email setup, spam filtering, account recovery, malware cleanup, device repairs, backup guidance, and SMB network monitoring across Edmonton. If you want hands-on help securing email on PCs, Macs, phones, or a small business domain, visit Nerds 2 You Edmonton.
Contact Nerds 2 You for quality professional service
Experience the difference with our dedicated team of experts ready to assist you. Whether you need immediate support or have questions about our services, we are here to help. Reach out today and let us provide you with the reliable service you deserve. Your satisfaction is our priority and we guarantee a prompt response to all inquiries.
Discover more from Nerds 2 You
Subscribe to get the latest posts sent to your email.